TL;DR
CISA urged organizations on Nov. 17 to patch Java4Shell, a memory-corruption flaw in an optimized Base64 decoder in certain Java runtimes. Exposure requires an affected runtime, an x86-64 processor with AVX-512 VBMI, and outside data reaching the decoder; vendors have released fixes. CISA’s record listed no exploitation as of Nov. 17, but organizations should check standalone and bundled Java installations.
CISA identifies the vulnerability as CVE-2026-114938 and says specially crafted Base64 input could crash the Java virtual machine and allow unauthenticated remote code execution. The flaw is in an optimized decoding routine in HotSpot, the Java engine used by OpenJDK-based distributions. The Canadian Centre for Cyber Security contributed to the alert.

Get everyday essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
The OpenJDK advisory lists Java 17, 21, 25 and 27 as affected, while Red Hat says the vulnerable code was introduced in OpenJDK 17.0.6. Red Hat states that OpenJDK 8 and 11 do not contain the code. Oracle’s advisory also identifies Oracle GraalVM and a specific Java 8 build, 8u511b33-perf; administrators should check their vendor’s advisory rather than assume every Java 8 installation is safe.
The processor and input conditions narrow exposure. Red Hat says ARM64 systems and x86-64 processors without AVX-512 VBMI are not affected. Oracle describes exploitation through data supplied to the relevant APIs, such as through a web service, and excludes untrusted Java Web Start applications and applets from its stated attack path. Internet-facing services that process outside input warrant prompt review.
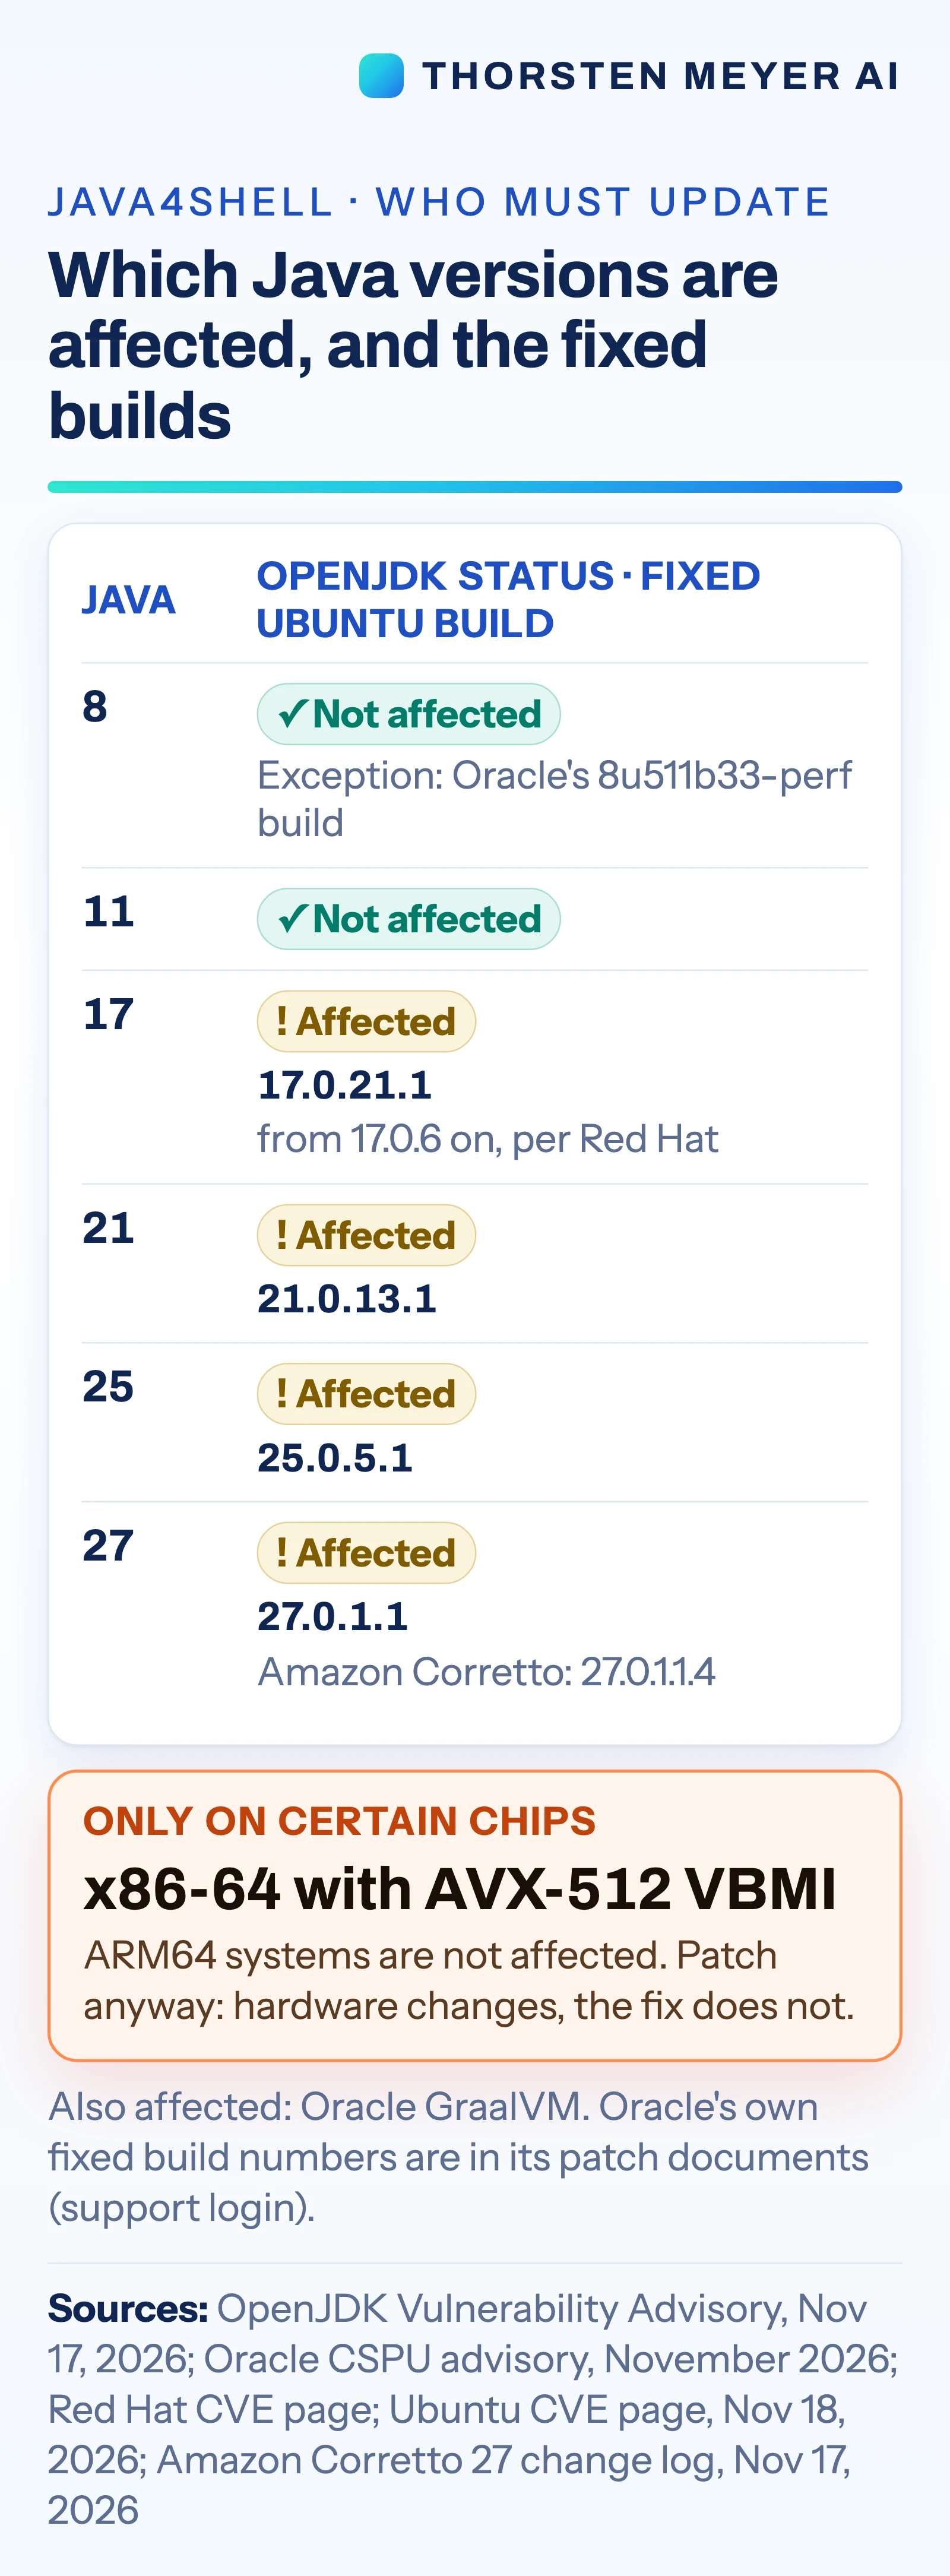
Which Java Services Face Risk
Java runs inside business applications, web services and products that may not advertise their runtime. A vulnerable Java component can therefore be present even when system administrators do not see a separately installed Java package. Containers and bundled software need checking alongside ordinary server installations.
CISA’s recommendation makes patching the practical response: install the relevant November vendor update, prioritizing internet-facing services. The processor requirement can help teams assess exposure, but it is not a substitute for updating an affected runtime. A patch removes the vulnerable code regardless of whether a particular machine meets the processor condition.
Severity ratings differ across sources. Oracle scores the flaw 8.1 out of 10 and calls it difficult to exploit; Red Hat rates it Critical at 9.8, while the researchers’ CVSS 4.0 score is 9.2. The National Vulnerability Database had not assigned a score in the supplied material. These are separate assessments, not evidence that the technical conditions differ.
Products Worth Considering

Logitech MX Brio Ultra HD 4K Webcam

Apple Watch SE 3 GPS + Cellular 40mm Smartwatch

Bose TV Speaker (2nd Gen) Compact Soundbar with Bluetooth and HDMI Connectivity
As an affiliate, we earn on qualifying purchases.
How Java4Shell Was Disclosed
CISA published its alert on Nov. 17, 2026, linking to Oracle’s November Critical Security Patch Update. Oracle says that package includes 655 new security patches across its products, including 11 for Java SE; Java4Shell received the highest score among those Java flaws. OpenJDK published an advisory on the same day.
The name Java4Shell echoes Log4Shell, the widely known vulnerability in a Java logging library. The name alone does not establish that the flaws work the same way or have comparable reach. The supplied advisories describe Java4Shell as a flaw in a particular HotSpot Base64 decoding routine with a processor requirement.
The documented path involves data reaching a Java API that uses the affected decoder, for example in a web service. This is not the old browser applet scenario. Red Hat’s guidance says systems on ARM64 or without the required x86-64 instruction set are not affected by this flaw.
““strongly urges organizations to immediately patch” CVE-2026-114938.”
— U.S. Cybersecurity and Infrastructure Security Agency
What Exposure Reports Confirm
CISA’s CVE record listed “Exploitation: none” on Nov. 17, and the flaw was absent from the agency’s known exploited vulnerabilities catalogue version dated Nov. 18. That records what CISA reported at those times; it does not establish that exploitation could not occur later or that every affected system is safe.
The supplied material does not identify how many systems are exposed or document confirmed attacks. The National Vulnerability Database had not scored the CVE, and the researchers said they were withholding product-specific attack chains. Organizations will need to confirm their own Java versions, processor capabilities, data flows and vendor patch status.
Check Runtimes and Apply Updates
Inventory Java runtimes on servers and workstations, then check the version and vendor against the relevant November advisory. Include Java embedded in applications, appliances and container images, and rebuild or update images that contain a vulnerable runtime. Start with internet-facing services that process untrusted input.
After patching, verify that the running service uses the updated runtime; updating a host package alone may not update a separately bundled copy. Follow vendor guidance for each product, and monitor CISA and vendor advisories for changes to exploitation status or technical details.
Key Questions
What is Java4Shell?
Java4Shell is the name used for CVE-2026-114938, a memory-corruption flaw in an optimized Base64 decoder in certain Java virtual machines.
Which Java versions are listed as affected?
The OpenJDK advisory lists Java 17, 21, 25 and 27. Oracle’s advisory also identifies Oracle GraalVM and the specific Java 8 build 8u511b33-perf. Check the advisory for your distribution and build.
Does every affected Java installation face the same exposure?
No. According to Red Hat, exploitation requires an x86-64 processor with AVX-512 VBMI; ARM64 systems and x86-64 processors without that feature are not affected. Untrusted data must also reach the relevant decoder.
Has Java4Shell been exploited?
CISA’s CVE record listed “Exploitation: none” on Nov. 17, 2026, and the flaw was not in its known exploited vulnerabilities catalogue dated Nov. 18. Those reports describe the status at those dates.
What should administrators do?
Install the November update from the Java vendor, prioritizing internet-facing systems. Check Java bundled into applications and container images as well as separately installed runtimes.
Source: Thorsten Meyer AI