TL;DR

Get everyday essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Microsoft’s November 10, 2026, Patch Tuesday release lists 1,094 Microsoft CVEs, including an Outlook flaw exploited before its fix. Paint requires separate attention: its October vulnerability was not fixed in the version Microsoft initially identified, and the corrected version may not yet be available to everyone. Microsoft has not said how many November fixes came from AI-assisted discovery.
Microsoft’s November 10 Patch Tuesday release lists 1,094 Microsoft CVEs, including an Outlook vulnerability that attackers exploited before a fix was available. A separate Paint vulnerability needs its own version check: the version Microsoft initially identified as fixed was still vulnerable, and the corrected version may not yet have reached some users, according to reporting by heise and PC Gamer.
Microsoft’s Security Update Guide release notes describe 1,094 Microsoft CVEs in the November release. Krebs on Security counted 1,093 flaws published on November 10; the difference is CVE-2026-109469, a Critical Entra Device Registration flaw published five days earlier. Microsoft says no customer action is required for that issue. The November data file contains entries from other vendors as well, but the source’s accounting separates those from Microsoft’s own vulnerabilities.
The most urgent item identified in the source is CVE-2026-124194 in Outlook. Opening a crafted file can expose a user’s NTLMv2 password hash, according to the source material. The Cybersecurity and Infrastructure Security Agency added the vulnerability to its catalog of exploited flaws on November 10. The source recommends prioritizing Outlook and Office updates, then reviewing the Critical server fixes relevant to each organization’s systems.
Paint’s CVE-2026-83844 is a separate case from the November Patch Tuesday count. Microsoft published the flaw on October 13. Heise reported that the Paint version Microsoft first named as fixed remained vulnerable; version 11.2609.401.0 was identified as the working version on November 6. PC Gamer reported that the corrected version was still not appearing for some users. Paint updates are obtained separately through the Microsoft Store, so installing Windows security updates alone may not resolve this app issue.
Separate Checks for Outlook and Paint
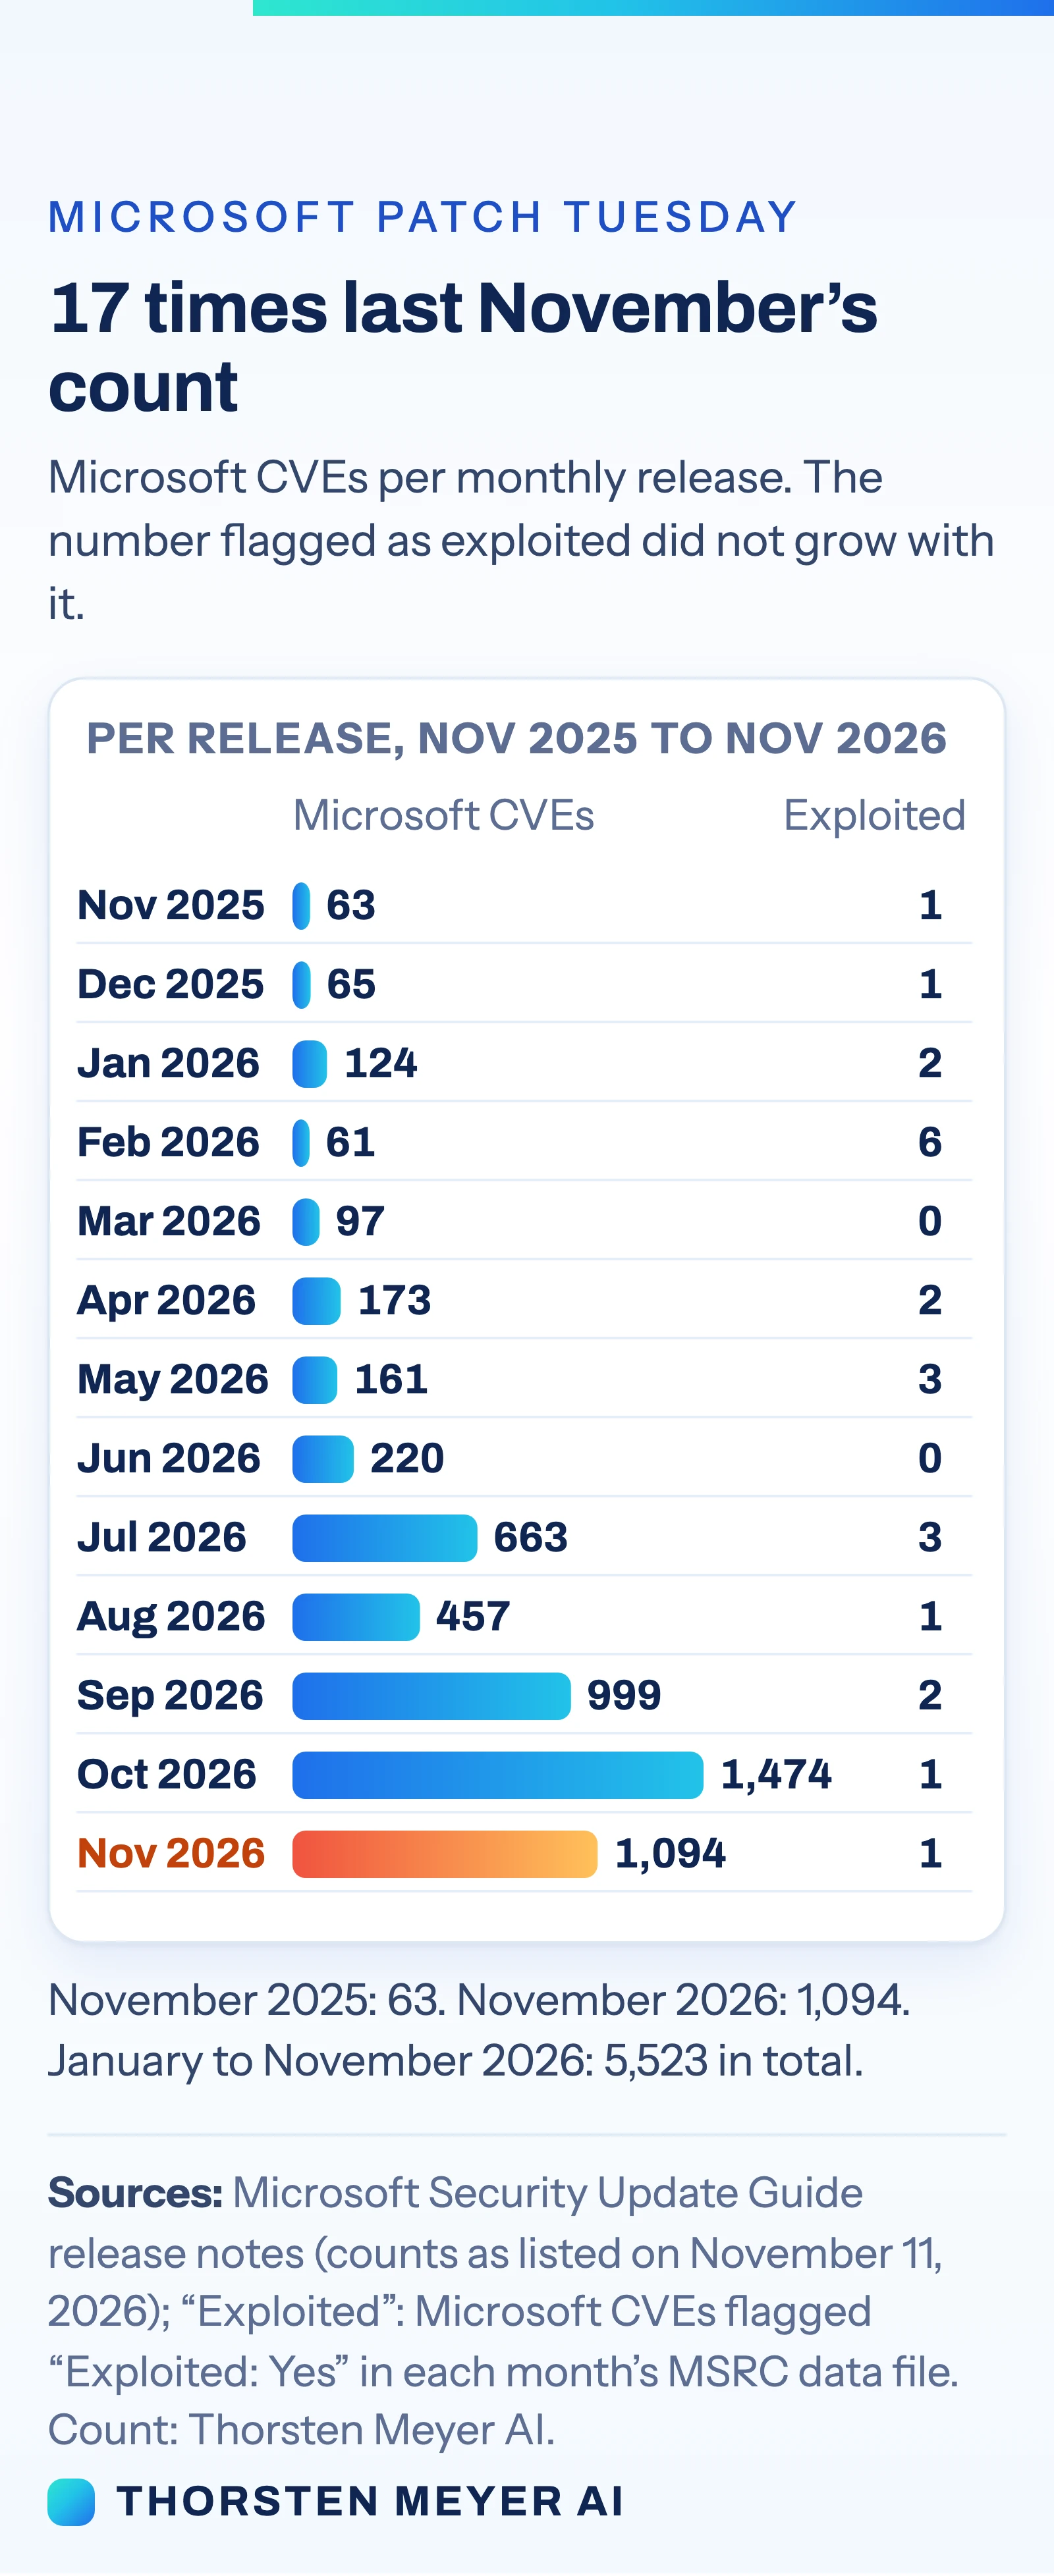
The release’s large CVE count makes prioritization important for administrators, but it does not mean every vulnerability has the same urgency or exposure. The source’s review of Microsoft’s monthly data found that flaws marked as exploited stayed between zero and six per month even as the total number of fixes rose; November had one. That count is a raw monthly observation, and the source does not establish that it captures every real-world attack.
Outlook and Paint call for different update checks. The Outlook flaw is identified as exploited and should be addressed through Microsoft’s security updates. Paint’s issue concerns a standalone app version that may not have arrived for every user. Checking the Store version separately can help users determine whether they have the version reported as fixed, while the available reporting does not confirm universal availability.
Products Worth Considering

Bose QuietComfort Wireless Noise-Cancelling Headphones, Sandstone

DJI Mini 3 Drone with DJI RC and 3-Axis Mechanical Gimbal

EcoFlow Delta 3 Max Portable Power Station with 220W Solar Panel, 2048Wh
As an affiliate, we earn on qualifying purchases.
How the Patch Count Grew
The release is part of a sharp rise in Microsoft’s monthly CVE totals. Microsoft’s release notes listed 63 Microsoft CVEs in November 2025, compared with 1,094 in November 2026. The source’s month-by-month figures rose to 220 in June 2026, 663 in July, 999 in September and 1,474 in October. Those counts describe Microsoft’s published CVEs and should not be read as a measure of how many were exploited.
Microsoft has attributed part of the increase to changes in vulnerability discovery. In April, Tom Gallagher, a Microsoft Security Response Center engineering vice president, wrote that AI can find more issues across a broader surface area. In May, Microsoft said advanced AI models were part of its discovery process, alongside more mature automation and broader participation by outside researchers. The company said it expected releases to keep trending larger for some time.
The November source counted 24 CVE credit lines that named a researcher using an AI model: 23 cited GLM from z.ai and one cited Claude. Those credits describe the named researchers’ work; they do not show which tools Microsoft used internally or establish AI’s share of the overall discovery effort.
“This release consists of 1094 Microsoft CVEs”
— Microsoft Security Update Guide, November 2026 release notes
Paint Availability Still Varies
The source material does not establish how many users have received Paint version 11.2609.401.0, or when it will be available to everyone. It also does not provide a complete technical account of the flaw or clarify whether every affected Paint installation is vulnerable in the same way. Users should check the app version and consult Microsoft’s current guidance for the issue.
Microsoft has not disclosed how many November fixes resulted from AI-assisted discovery. Researcher credit lines identify some external use of AI, but they cannot determine the contribution of Microsoft’s internal tools. The difference between Microsoft’s 1,094 release-note total and Krebs on Security’s 1,093 count reflects the earlier Entra issue in the source’s accounting.
Check the Relevant App Versions
Organizations should review Microsoft’s November security guidance, apply the Outlook and Office fixes, and assess the Critical server vulnerabilities against their own systems. For Paint, users can check for updates in the Microsoft Store and confirm whether the installed version is 11.2609.401.0, the version the source identifies as corrected. Further Microsoft guidance or broader Store availability may clarify how quickly affected users can receive the Paint fix.
Key Questions
What did Microsoft release on November 10?
Microsoft’s release notes list 1,094 Microsoft CVEs in its November 2026 Patch Tuesday release. Krebs on Security counted 1,093 published that day; the source attributes the difference to an Entra flaw published November 5.
Why does Paint need a separate fix check?
Paint’s CVE-2026-83844 was published in October, and the version initially identified as fixed reportedly remained vulnerable. The corrected version is 11.2609.401.0, but PC Gamer reported that it was not yet showing up for some users. Check for Paint updates through the Microsoft Store.
Which November vulnerability was reported as exploited?
The source identifies CVE-2026-124194 in Outlook as exploited before its fix. Opening a crafted file can expose a user’s NTLMv2 password hash, and CISA added the flaw to its exploited-vulnerability catalog on November 10.
Did AI account for most of the November fixes?
Microsoft has said AI tools contribute to vulnerability discovery, along with automation and outside researchers. It has not disclosed how many November fixes came from AI. The source found 24 researcher credit lines that named AI use, but those do not reveal Microsoft’s internal tools.
Source: Thorsten Meyer AI