TL;DR
An article dated Nov. 13, 2026, describes a hypothetical use of Thrymvault, a self-hosted workspace, to let AI agents assist with defense suppliers’ engineering and business workflows. Thrymvault has no defense customers, is not approved for classified information and has no security certification; the scenario outlines controls a real deployment would need.
In the scenario, an engineer files a request to change a connector supplier. An agent drafts an impact summary and links affected requirements, while a review board comments and requests input. A named, signed-in person sets the request to approved; the workspace records the activity and saves a new version. The article stresses that this status is not a cryptographic signature.

Get everyday essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Meyer says the proposed guardrails include owner-approved applications, keys limited to one workspace, agent changes labeled with the application that made them, and no ability for agents to delete records. The product description also lists two-factor sign-in, per-item sharing for guests, activity logs, a change feed and version history. The article cites Thrymvault’s agent integration guide, README and development log as sources for those current features.
The article distinguishes features it says are built from work still being rolled out. It describes a current setup of one machine with nightly backups copied to a second machine; an hourly backup and manually operated standby process are planned. Live testing of webhooks to an internal machine and long-running agent work with a real model are also not complete, according to the source.
Example 2 · Corvus ISR · scenario
Every public claim linked to its measurement
How the Corvus ISR team would keep its website honest on Thrymvault. Agents file and link the evidence. People decide what may be claimed.
Release card: next releaseRelease board
A benchmark run lands as a page.
via Evaluation assistantThe results are linked to the release card.
A degradation finding from the public demonstration becomes a card.
A claim without a current measurement is flagged.
People decide: measure again, change the claim or take it down.
Claims register
On the release card
Benchmark run page · via Evaluation assistant
Linked to this release · via Evaluation assistant
Card: degradation finding from the demonstration · owner: a named engineer
Decision: measure again before release · by the release board
No public claim without a current measurement. A flagged claim is never kept silently.
Source: Corvus ISR public website (corvusisr.com), read November 2026; Thrymvault README and agent integration guide, November 2026. A scenario: Corvus ISR does not run its work on Thrymvault today.
Animation: Thorsten Meyer AI
Controls Before Agents Touch Records
The scenario highlights a practical issue for organizations handling regulated or sensitive records: an agent that can read broadly or make untraceable changes may be unsuitable even if it can speed up routine work. Controls such as limited access, visible attribution and preserved history can help people review what an agent did and identify who made the decisions.
Those controls alone do not establish that a system is fit for defense work. The article says Thrymvault has no certification or accreditation and is not a records-management system of record. A real deployment would need its own security evaluation and approval against the requirements that apply to the information and organization involved.
Products Worth Considering

Bose TV Speaker (2nd Gen) – Compact Soundbar with Bluetooth and HDMI‑ARC Connectivity, Clear Dialogue, Dolby Atmos, Deep Bass, Remote Contro

Apple MacBook Air 15-inch Laptop with M5 Chip, 16GB Memory, 512GB SSD, Midnight
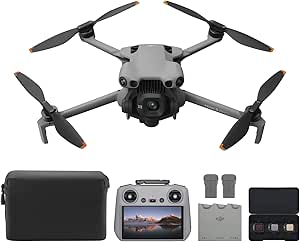
DJI Mini 5 Pro Fly More Combo with DJI RC 2
As an affiliate, we earn on qualifying purchases.
A Product Still Under Development
The article frames Thrymvault as a workspace for the back office of a hypothetical defense supplier, including bids, engineering change control, export and supplier screening queues, program boards and runbooks. It also describes possible use by two defense technology projects Meyer is building, VigilSAR and Corvus ISR, while stating that neither project currently runs its work on the platform.
The source reports that the workspace has pages, databases with several views, comments, relations and version history, alongside an MCP server with 20 tools, a REST API and a command-line tool. It says 5,656 automated tests had run at the last deployment. That test count is a product development detail; it does not amount to a formal security assessment or defense approval.
Deployment Readiness Remains Open
No customer deployment, defense use or classified data handling is described. The source says Thrymvault has not undergone a formal security evaluation, is not tested for air-gapped operation, and has no certification or accreditation. It does not specify which security standards a future deployment would pursue or whether the planned backup, standby and monitoring arrangements will meet operational needs.
The piece is a thought experiment, so it offers no measured results for agent accuracy, time saved, or error rates in defense workflows. It also does not identify a real supplier, program or government customer. Its product claims are attributed to the company’s own documentation and development log.
Testing and Approval Still Ahead
The source describes several development steps still pending, including live testing of internal webhook delivery and rollout of the standby machine, hourly backups, monitoring and team access. It does not provide dates for those milestones or announce a defense customer evaluation.
Before use with sensitive defense records, a real deployment would still need an appropriate security review, authorization for its intended information and environment, and evidence that its access controls, audit history, backup process and human approval steps work as required. No such approval is reported in the article.
Key Questions
Is Thrymvault being used by a defense company?
No. The source says Thrymvault has no defense customers and describes only a hypothetical scenario.
Can Thrymvault handle classified information?
The article says it is not approved for classified information and has no certification or accreditation of any kind.
What would the AI agents do in the scenario?
They would draft an engineering change impact summary, link affected requirements and flag missing reviews. People would review and approve the change.
What safeguards does the article describe?
It lists owner-approved applications, workspace-limited keys, agent attribution in the change history and a prohibition on agent deletions. It also describes two-factor sign-in and per-item sharing.
What remains unfinished?
The source says backup and standby improvements are being rolled out, internal webhook delivery has not been tested live, and long-running agent work with a real model has not been tested. It reports no formal security evaluation.
Source: Thorsten Meyer AI